
Introduction to Access Control
Access control is a fundamental concept that refers to the processes and mechanisms used to manage and regulate who can access information, resources, and areas within an organization. This practice is particularly significant for businesses in the United Kingdom, as it helps ensure that sensitive data and critical assets are protected against unauthorized access and exploitation.
Implementing effective access control measures involves defining user roles, permissions, and restrictions. These mechanisms not only help safeguard confidential information but also serve to maintain compliance with various regulatory frameworks that govern data protection in the UK, such as the General Data Protection Regulation (GDPR). By establishing clear access rights and responsibilities, organizations can enhance their security posture and foster a culture of accountability among employees.
The importance of access control cannot be overstated. In today’s digital landscape, where data breaches and cyber threats are prevalent, businesses must prioritize the security of their critical information. Access control systems help to minimize potential risks by ensuring that only authorized individuals are granted entry to specific areas and information. This is essential for preventing data leaks, protecting proprietary information, and maintaining overall organizational integrity.
Furthermore, access control mechanisms are not limited to physical spaces but also encompass digital environments. For businesses leveraging cloud services or operating online, ensuring that appropriate access controls are in place is vital. This holistic approach to access management helps organizations to maintain their competitive edge while safeguarding their assets.
In conclusion, access control is a key component of operational security for businesses in the UK. By regulating access to sensitive information and crucial resources, organizations can mitigate risks and enhance their overall security framework.
Types of Access Control Systems
Access control systems are essential for maintaining security and protecting sensitive information within businesses in the United Kingdom. These systems regulate who can view or use resources in a computing environment. There are three primary types of access control systems that organizations utilize: Discretionary Access Control (DAC), Mandatory Access Control (MAC), and Role-Based Access Control (RBAC). Each of these systems comes with its own set of advantages and disadvantages.
Discretionary Access Control (DAC) allows owners of resources to determine who can access specific entities. With this approach, users have the authority to grant or restrict access to their files or systems. One of the key advantages of DAC is its flexibility, as users can easily manage permissions according to their needs. However, this flexibility can also result in security vulnerabilities if users do not properly manage permissions, potentially leading to unauthorized access.
Mandatory Access Control (MAC), on the other hand, is more structured and stringent. In this model, access rights are regulated by a central authority based on multiple security levels. Users cannot change access permissions as they do in DAC, which is beneficial for protecting sensitive data. However, MAC can be overly restrictive and may hinder collaboration and productivity within an organization, as users find it difficult to access necessary information.
Role-Based Access Control (RBAC) combines elements of both DAC and MAC by assigning permissions based on the roles of individual users within an organization. This means that access rights are grouped by role rather than individual user needs. The main advantage of RBAC is its ability to minimize the complexity of permission management, enhancing both security and efficiency. However, it requires careful role definition and management, which can become complex as organizations grow and change.
In conclusion, businesses in the UK must carefully consider these access control systems to determine which framework best meets their security policies and operational needs. Each system has its pros and cons, and the optimal choice depends on the specific context of the organization’s operations.
Legal Regulations and Compliance
Access control is a crucial aspect of managing sensitive information within organizations in the United Kingdom. Businesses must align their practices with various legal regulations and frameworks that govern how access to data is handled. Among these, data protection laws play a pivotal role in ensuring that personal information is safeguarded against unauthorized access and breaches.
One of the primary regulatory frameworks influencing access control is the General Data Protection Regulation (GDPR), which came into effect in May 2018. This regulation applies to any organization that processes the personal data of individuals residing in the UK, as well as other jurisdictions. The GDPR mandates that businesses implement adequate security measures to protect sensitive personal information, which directly impacts how access rights are assigned and managed.
Furthermore, organizations must ensure that access control measures include principles such as data minimization and purpose limitation. For instance, employees should only have access to the information necessary for their job roles, thereby reducing the risk of unauthorized data exposure. The implications of failing to comply with these regulations can result in substantial fines and reputational damage, emphasizing the importance of robust access control measures within businesses.
Additionally, the Data Protection Act 2018 complements the GDPR by providing a comprehensive framework for data protection in the UK. This act outlines specific requirements for handling personal data and establishes the role of the Information Commissioner’s Office (ICO) in enforcing compliance. Businesses must not only have policies in place for data handling but also regularly review and update their access control mechanisms to remain compliant with evolving legal standards.
Organizations should be proactive in educating their staff about the importance of access control and data protection. Regular training and awareness programs can help ensure that employees understand their responsibilities regarding data handling and the measures in place to protect sensitive information. By doing so, businesses can foster a culture of compliance and accountability, which is essential for safeguarding personal data in today’s data-driven environment.
Best Practices for Implementing Access Control
Establishing effective access control measures is crucial for businesses in the United Kingdom to protect sensitive information and maintain operational integrity. One of the cornerstone best practices is employee training. All employees should receive comprehensive training that outlines the access control policies and procedures applicable within the organization. This training should ensure that staff understand the significance of safeguarding access credentials and the potential consequences of security breaches.
Regular audits play a vital role in maintaining the effectiveness of access control systems. Businesses should conduct periodic reviews of their access control policies to assess compliance and identify any gaps in security. These audits can help pinpoint instances where access privileges may need adjustment, especially when employees change roles or leave the organization. By routinely evaluating access controls, businesses reduce the risk of unauthorized access to sensitive resources.
Maintaining accurate access logs is another best practice that cannot be overlooked. Access logs provide a record of who accessed what resources and when. This information can be invaluable during security incidents as it allows businesses to trace back unauthorized access attempts or potential breaches. It is essential to implement a logging system that captures relevant data points while ensuring that such data is stored securely and in compliance with data protection regulations.
Additionally, businesses should consider implementing the principle of least privilege (PoLP) as part of their access control strategy. This principle dictates that employees should only have access to the resources necessary for their roles, minimizing the chances of data exposure. By adhering to this principle, organizations can better shield against both internal and external threats.
In conclusion, the implementation of disciplined access control measures, employee training, regular audits, and robust access logging is essential for the protection of business assets in the UK. Adopting these best practices helps ensure that access control systems effectively mitigate risks and enhance overall security, fostering a safer business environment.
Choosing the Right Access Control Technologies
Access control systems are vital for ensuring the security of businesses in the United Kingdom. Selecting the appropriate technology is crucial for effective management of physical and digital access. Among the most common options are key card systems, biometric authentication, and mobile access solutions, each presenting unique benefits and challenges.
Key card systems are widely used due to their ease of implementation and cost-effectiveness. They operate by granting access based on the presence of a programmed card, which can be easily issued and deactivated. However, one challenge associated with key card systems is the potential for loss or theft, which could compromise security if not managed properly.
Biometric technology, which includes fingerprint scanning, facial recognition, and iris scanning, offers a higher level of security. This technology verifies identity based on unique biological characteristics, making it difficult to replicate. The primary benefit of biometrics is the reduction of unauthorized access; however, issues such as privacy concerns, the need for thorough data protection measures, and the high initial investment can pose significant challenges for businesses considering this option.
Mobile access solutions are gaining popularity, leveraging smartphones to control entry to facilities. This technology allows users to unlock doors with their phones, often via an application. The convenience and integration with existing digital systems are major advantages. Nevertheless, reliance on mobile connectivity and potential concerns regarding app security can limit this option’s effectiveness.
When determining which access control technology to employ, businesses should evaluate their specific security needs, budget constraints, and the potential vulnerabilities of each system. A comprehensive assessment will aid organizations in making an informed decision that aligns with their operational requirements while maximizing security.
The Role of Physical Access Control
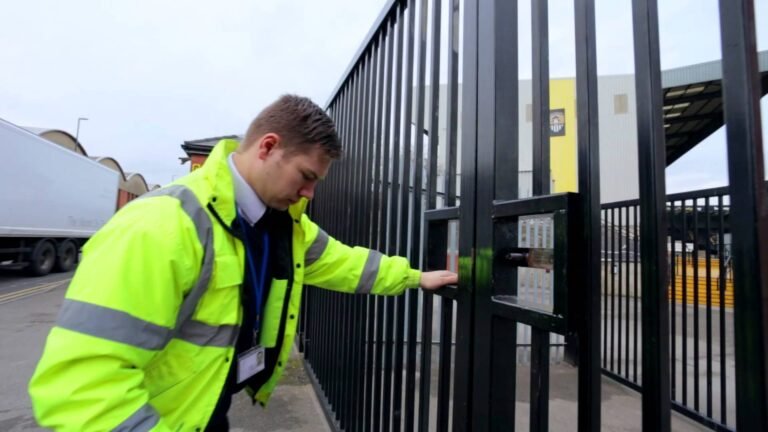
Physical access control is a fundamental component of a comprehensive security strategy for businesses in the United Kingdom. It refers to the measures put in place to restrict unauthorized individuals from accessing sensitive areas within a facility. These measures can include locks, security personnel, surveillance systems, and other tangible barriers that physically deter intruders and unauthorized personnel from entering restricted zones.
One of the primary instruments of physical access control is the locking mechanism. Traditional locks, combination locks, and electronic access locks play a crucial role in safeguarding premises. Electronic locks, in particular, offer enhanced security features, including key card access and biometric verification, which are more difficult to bypass compared to conventional locks. This level of security significantly reduces the risk of unauthorized access and fortifies the overall security framework of the business.
In addition to locking systems, the presence of security personnel is invaluable in reinforcing physical access control. Trained security staff can monitor and manage access to critical areas, ensuring that only authorized individuals enter these spaces. Their ability to assess situations in real-time and respond to potential security threats further enhances safety. Moreover, security personnel serve as a physical deterrent, as their visible presence can discourage would-be intruders.
Surveillance systems, such as CCTV cameras, complement physical access control measures by providing continuous monitoring of the premises. These systems not only capture incidents as they occur but also serve as a deterrent to unauthorized activity. When individuals are aware that they are being recorded, they are less likely to attempt unauthorized entry. The integration of surveillance technology with access control systems allows for a comprehensive approach to security, facilitating a quick response to any breaches.
The synergy between physical and digital access control systems is essential. While digital measures offer an efficient way to manage access through logging and monitoring capabilities, physical controls act as the last line of defense. Businesses must recognize the importance of combining these systems to provide a multi-layered security approach that effectively mitigates risks associated with unauthorized access.
Challenges and Solutions in Access Control Management
Access control management is a critical aspect for businesses in the United Kingdom, yet it presents numerous challenges that can significantly impact operations. One of the foremost challenges is the presence of insider threats. Employees with legitimate access may pose a risk, either intentionally or accidentally. This risk is amplified in environments where sensitive information is handled, making it imperative for businesses to implement stringent access controls.
Another common issue is compliance with various data protection regulations, such as the UK General Data Protection Regulation (GDPR). Non-compliance can lead to severe penalties, making it essential for businesses to establish robust access control policies that align with these regulations. Maintaining compliance requires continuous monitoring and regular updates to access permissions, which can be resource-intensive.
Furthermore, businesses often struggle with maintaining up-to-date access control systems due to fast-paced technological advancements. Legacy systems may not effectively handle modern security needs, leading to vulnerabilities. Companies must assess their current systems and be willing to invest in upgrades or new solutions to enhance security.
To counter these challenges, organizations can adopt several solutions. For instance, implementing a role-based access control (RBAC) system can help in reducing insider threats by restricting access based on job functions. This approach limits the exposure of sensitive information to only those who genuinely require it for their role.
Moreover, conducting regular training and awareness programs for employees can mitigate risks associated with insider threats. By understanding their roles in maintaining security, employees become more vigilant, reducing the likelihood of accidental data breaches.
Lastly, utilizing modern technologies such as multi-factor authentication (MFA) can strengthen access control measures against unauthorized access. By combining something the user knows (like a password) with something they have (like a mobile device), businesses can significantly bolster their defense against potential security threats.
The Future of Access Control in the UK
The landscape of access control is rapidly evolving, bringing new trends and innovative technologies to the forefront for businesses across the United Kingdom. This transformation is primarily driven by the need for enhanced security measures, as businesses seek to protect sensitive information and assets amidst an increasing threat of cyberattacks and unauthorized access.
One significant trend in access control is the integration of biometric technology. This includes fingerprint recognition, facial recognition, and iris scanning, which provide a more secure alternative to traditional access methods such as key cards and PIN codes. Biometric systems are not only harder to counterfeit but also offer convenience, as users do not need to remember complex combinations.
Additionally, the adoption of cloud-based access control solutions is on the rise. These systems allow businesses to manage access remotely, offering greater flexibility and reduced operating costs. With cloud technology, updates can be implemented quickly, and access rights can be adjusted in real-time, accommodating the dynamic needs of modern work environments.
Moreover, the rise of the Internet of Things (IoT) is influencing access control strategies significantly. Smart devices can be integrated with security systems, enabling businesses to create a connected environment where access control can be managed seamlessly through mobile applications. This interconnected approach not only enhances security but also streamlines overall operations within the organization.
As we look towards the future, it is evident that businesses in the UK must embrace these innovative access control solutions. By doing so, they can not only protect their assets more effectively but also position themselves as leaders in security and technology adaptation. Staying ahead of these trends will be vital for businesses aiming to secure their premises against both physical and cyber threats.
Conclusion and Final Thoughts
Access control systems play a vital role in safeguarding the assets and information of businesses across the United Kingdom. As discussed throughout this blog, the implementation and maintenance of robust access control measures are essential for protecting against unauthorized access and potential security breaches. Businesses must recognize that having an effective access control strategy not only secures physical spaces but also preserves sensitive data. This multifaceted approach helps to mitigate risks and enhance overall business resilience.
Moreover, staying compliant with regulations and laws governing data protection is crucial. Businesses that fail to prioritize access control systems may expose themselves to legal liabilities and reputational damage. Therefore, it is imperative for organizations to regularly evaluate their existing security frameworks and adjust them in response to evolving threats and technological advancements. By conducting routine assessments and security audits, businesses can identify vulnerabilities and reinforce their access control protocols.
Organizations should also invest in employee training and awareness programs. Ensuring that staff members understand the significance of access control and how to adhere to established protocols can significantly reduce the likelihood of errors or security lapses. Ultimately, fostering a culture of security awareness within the organization enhances the effectiveness of access control measures.
In conclusion, the importance of robust access control systems for businesses in the UK cannot be overstated. Companies must remain vigilant and proactive in their security strategies, continually adapting to new challenges in the landscape of access control. By prioritizing secure access to facilities and data, businesses can protect their assets and ensure long-term success in an increasingly complex environment.


0 Comments